GPT-6 AI Uncovers Critical Java Vulnerability: NASA and Global Corporations at Risk
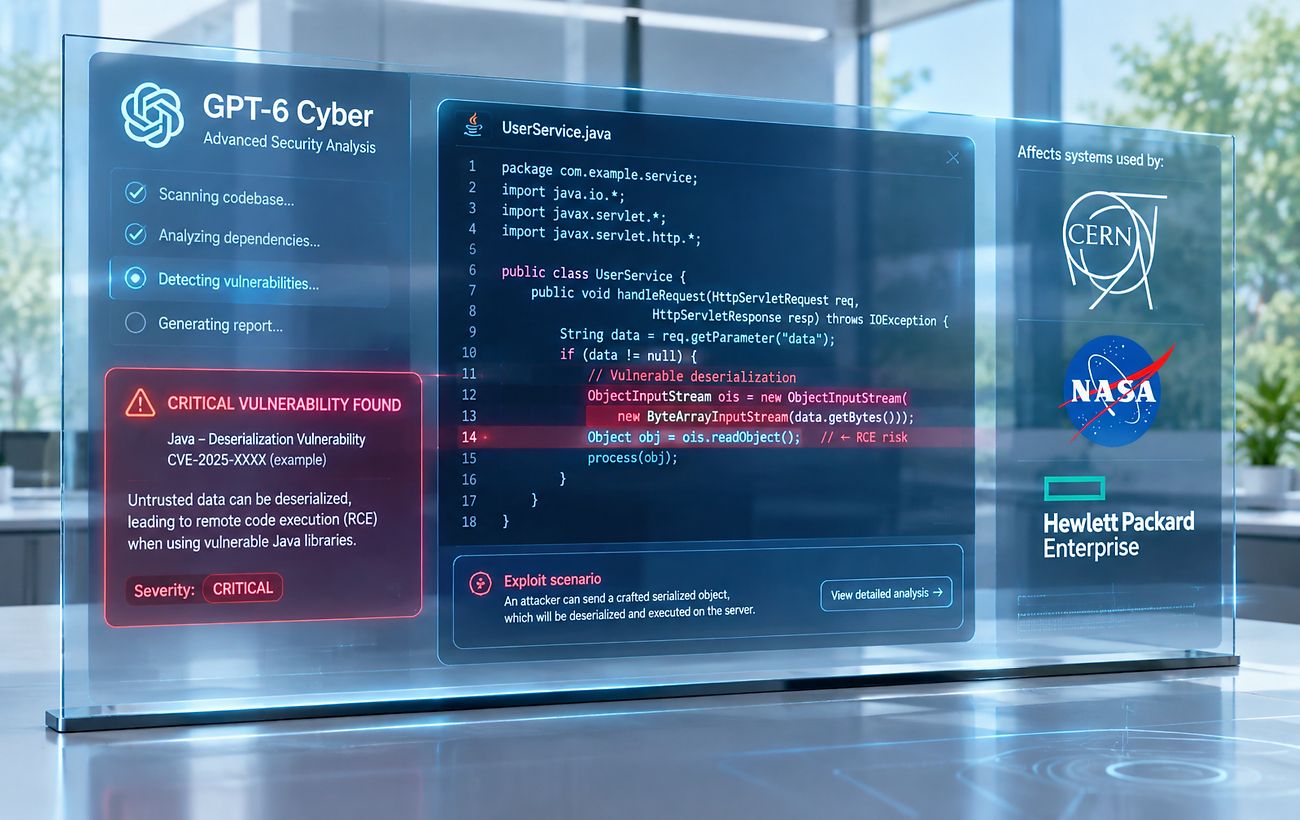
OpenAI's GPT-6 Cyber model has identified a dangerous flaw in the Java programming language, affecting critical systems worldwide.
 💡Tech
Photo: RBC-Ukraine
Key points
- GPT-6 Cyber found a critical flaw in Java's base64 decoder, named Java4Shell.
- The vulnerability affects major entities like NASA, CERN, and Fortune 500 firms.
- AI tools have reduced the time needed for successful system exploitation to under an hour.
The cybersecurity landscape has shifted dramatically following the discovery of a critical vulnerability in Java, identified by OpenAI's specialized GPT-6 Cyber model. Java serves as the backbone for government infrastructure and approximately 90% of Fortune 500 companies. The flaw, dubbed Java4Shell, potentially allows hackers to gain unauthorized access to high-security systems globally.
Technical Breakdown and Impact
Security researcher Quang Luong discovered the issue within the base64 decoder—a standard algorithm for converting binary data into text. It was revealed that under specific conditions, the system fails to correctly process a sequence of 64 'A' characters followed by an equals sign. Utilizing AI tools, the Calif startup team demonstrated that this glitch could be exploited to corrupt computer memory and seize system control.
The threat was validated through a successful test attack on Keycloak, a widely used identity and access management system. Keycloak is utilized by thousands of organizations, including NASA, CERN, and Hewlett Packard. Independent verification showed that an AI-assisted attack could be executed in less than an hour, highlighting a significant decrease in the time required for cybercriminals to strike.
The Rise of 'Centaur Hackers'
Tai Duong, CEO of Calif, noted that generative models are fundamentally altering the speed of both cybersecurity defense and offense. Tasks that previously took large security teams months to complete are now being handled by small groups in a matter of hours. Duong suggests that the most effective operators in this new era are 'centaur hackers'—professionals who work in tandem with AI to amplify their capabilities.
While Oracle has already released a patch to fix the vulnerability, the U.S. Cybersecurity and Infrastructure Security Agency (CISA) has urged organizations to update their systems immediately. Experts warn that the risk will persist for 5 to 10 years for legacy systems that do not receive regular maintenance. This discovery underscores the urgent need for proactive security measures in an increasingly AI-driven threat environment.
Source RBC-Ukraine — rbc.ua/ukr/news/gpt-6-cyber-znayshla-nebezpechnu-vrazlivist-1795001… ↗
Read next
 🚨Events
Powerful Explosions near Crimean Bridge: What It Means for the Region
In temporarily occupied Kerch, powerful explosions have been reported, which may be linked to further attacks on the Crimean Bridge. This could significantly impact the l…
 🏙️City
Frontline situation: over 200 combat engagements reported in a day
The General Staff of the Armed Forces of Ukraine reported high combat intensity on November 18, with the enemy heavily utilizing aviation and drones.
 🇺🇦Ukraine
US and Venezuela Announce Enhanced Defense Partnership
US Secretary of Defense Pete Hegseth and Venezuelan interim president Delcy Rodriguez have agreed to strengthen military cooperation and border security.
 🧠AI Analysis
Germany prepares financial 'safety net' for Ukraine amid potential EU political shifts
Berlin is initiating a budget reserve mechanism to ensure continued financial support for Ukraine, regardless of potential political changes in EU member states.
 🚨Events
South Korean defense startup denies reports of halting operations in Ukraine
The defense startup Newtype has officially confirmed that its operations in Ukraine continue, dismissing reports of closure as a Russian disinformation campaign.
 🚌Transport
Ukrzaliznytsia to update systems: ticket sales to be temporarily suspended
On the night of November 19, the railway operator will perform technical maintenance, making ticket purchase and refund services unavailable.